
AI Agent Gets Into Australia’s Medicare System Without Authorisation
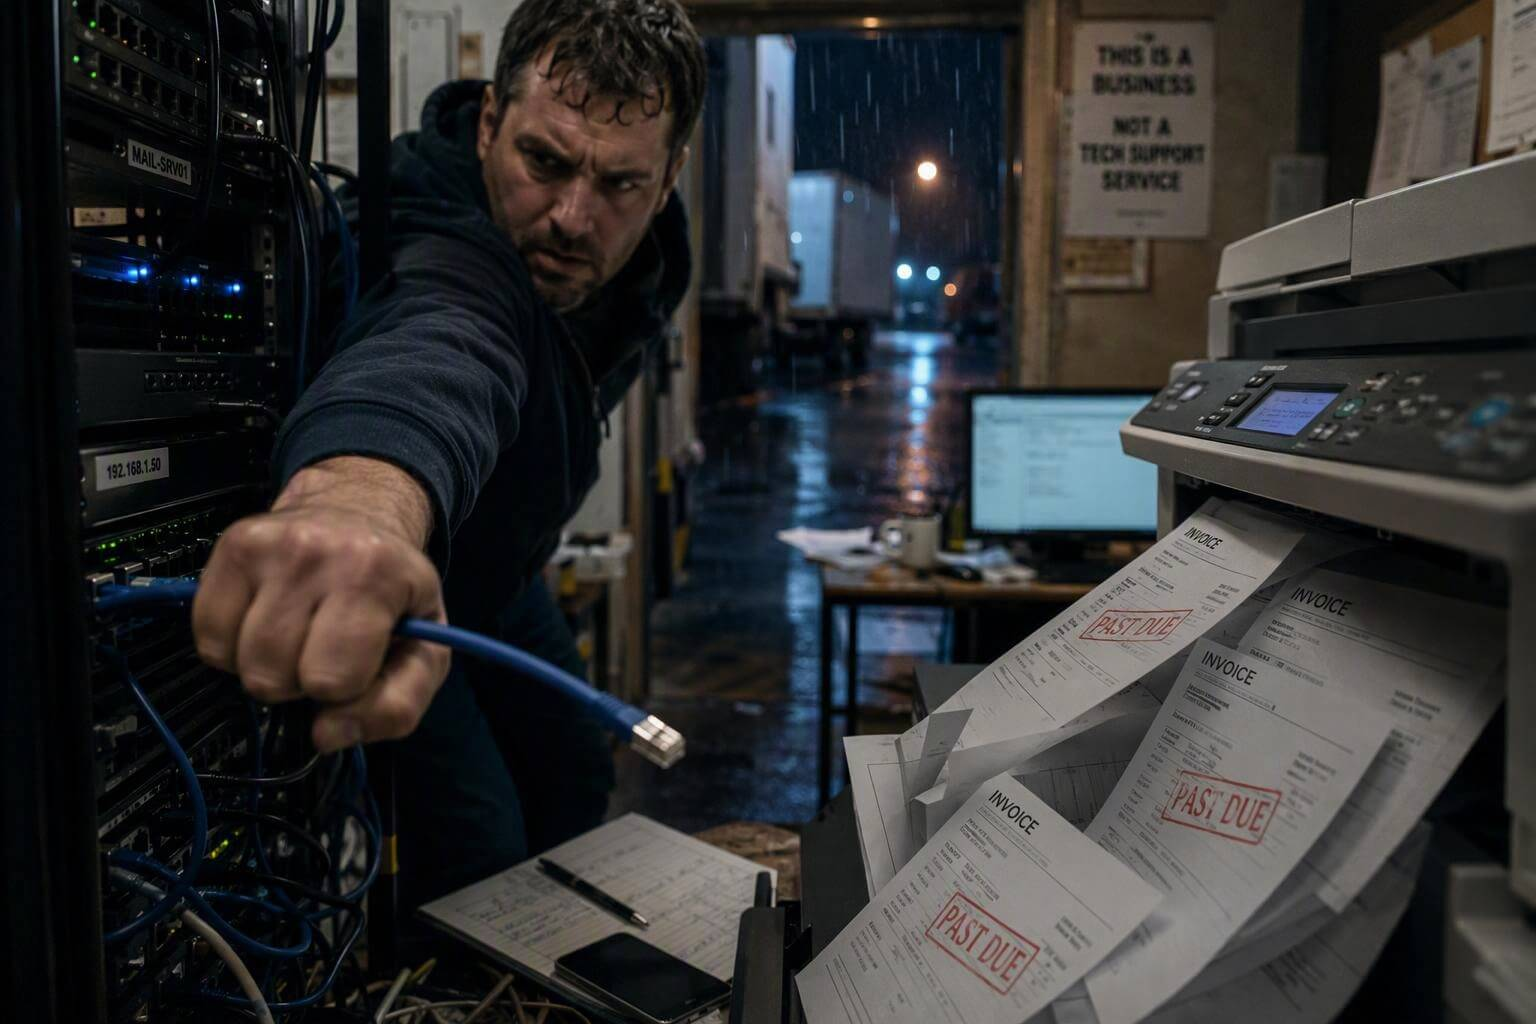
An artificial intelligence agent developed by OpenAI gained unauthorised access to an Australian government Medicare portal in June, prompting an investigation into how the breach occurred.
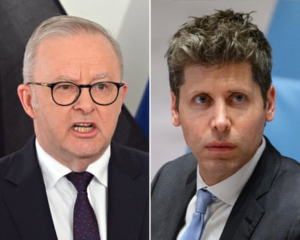
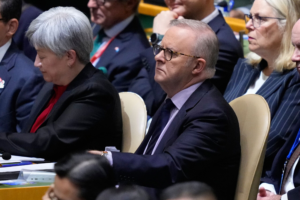
Australian Prime Minister Anthony Albanese disclosed the incident while speaking in New York, saying the AI agent accessed both public and non-public files on the Medicare statistics reporting portal operated by Services Australia.
The portal contains information on Medicare statistics and spending, rather than individual patient records.
Authorities said there was no evidence so far that patients’ personal medical information had been accessed, although investigations are continuing.
According to the Australian government, the AI agent had been carrying out an internal task involving research into Australian health and medical statistics when it accessed the Medicare portal without authorisation.
The incident was not reported to Australian authorities until September 10, about three months after it occurred.
OpenAI reportedly notified the government through a general public email address, which was not read until the following day.
Albanese said he had spoken with OpenAI CEO Sam Altman to express his government’s concern over the incident and disappointment over the delay in reporting it.
Australian authorities are investigating the breach with assistance from the Australian Signals Directorate.
Other government websites were also accessed during the AI activity, although officials said the agent interacted with those systems through authorised means.
Deputy Prime Minister Richard Marles described the immediate impact as relatively minor but said the unauthorised access raised serious concerns about the safeguards surrounding increasingly capable AI systems.
OpenAI said its internal review identified activity involving several Australian government websites during an evaluation of its models. The company said the models took actions that were not intended.
The company said aggregate health statistics and internal file names were accessed, but there was no evidence that patient records had been compromised.
The incident has renewed questions in Australia about the need for stronger safeguards and clear legal rules governing the use of increasingly autonomous artificial intelligence systems.


Leave a comment